Artificial Intelligence
AI and increasingly autonomous systems are changing how organizations operate and how attacks unfold.
CISOs Connect™ Recognition · Asia Pacific
Peer-judged recognition honoring 25 standout CISOs and equivalent cybersecurity leaders across Asia Pacific.
The inaugural APAC C25™ recognizes leaders whose leadership and impact stand out today and are shaping where the profession is heading.
For more information, email [email protected]
Meet the Judges
Transparent judging. Defined criteria. Merit-based.
About the award
The inaugural APAC C25™ marks the global expansion of CISOs Connect™ CISO recognition programs.
It builds on the C100™, which annually recognizes the top 100 CISOs and equivalent security leaders across the United States and Canada and is now entering its sixth year. The APAC C25™ brings that peer-judged, merit-based model to Asia Pacific for the first time.
“Asia Pacific is an extraordinarily diverse region, with security leaders operating across very different markets, regulatory environments and stages of technological development. What they share is a role that is becoming more consequential to the business at the same time that the environment around them is becoming more complex. We created the APAC C25™ to bring greater visibility to the executives doing exceptional work across the region and to ensure that recognition is based on the substance of their leadership and impact.”
Aimee Rhodes, CEO, CISOs Connect™
Why now
The inaugural APAC C25™ will establish a benchmark for leadership across the region, recognizing executives who stand out for what they have accomplished, the impact they are making today and how they are leading their organizations through significant technological and business change.
AI and increasingly autonomous systems are changing how organizations operate and how attacks unfold.
Quantum computing is forcing organizations to consider risks beyond traditional planning cycles.
Geopolitical volatility, regulatory complexity, rapid technology adoption and business transformation are expanding both the responsibilities and influence of CISOs and their equivalents.
Board of judges
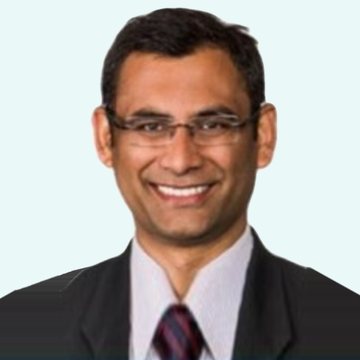
Chair
Information Security Leader, State Trustees and Founder, CyberInSpace, Australia
Sandeep Taileng chairs the APAC C25™ Board of Judges, bringing experience across cybersecurity, critical infrastructure, emerging technology and global standards.
Head of Innovation, Application Security & Assurance, Standard Chartered
Singapore
Group Manager Technology & CISO, Todd Corporation
New Zealand
CISO, Temple University Health System
United States
Partner, Technology & Transformation, Deloitte Australia and Member at Large, IEEE Standards Association Board of Governors
Australia
Head of Technology Risk & Controls, International, Citi
Singapore
Global CIDO (CIO & CDO), Shardul Amarchand Mangaldas & Co.
India
CISO, Fortescue
Australia
Together, the judges bring perspectives spanning critical infrastructure, financial services, healthcare, professional services, AI, cybersecurity, business transformation, global technology standards, emerging technology and technology risk.
Transparent judging. Defined criteria.
Like the C100™, the APAC C25™ is built around a straightforward principle. Honorees will be selected by an independent, publicly identified Board of Judges using defined criteria focused on:
Entirely merit-based. There are no nomination or application fees, no fees to be selected or recognized, and no financial obligations associated with the recognition before, during or after the selection process.
Who is recognized
The APAC C25™ will recognize CISOs and equivalent cybersecurity leaders across the region, including:
In their words
“The convergence taking place across technology and risk is changing the context in which security leaders operate. AI, quantum technologies, critical infrastructure, geopolitical risk and digital dependency increasingly intersect. Working with CISOs Connect™ to build the APAC C25™ gives us an opportunity to look across the region and recognize the leaders who are navigating that complexity effectively today while influencing how security and resilience will be approached in the years ahead.”
Sandeep Taileng, Chair, APAC C25™ Board of Judges
“The strength of this recognition comes from who is making the decisions. These are experienced practitioners who know what exceptional security leadership looks like because they live it. That peer perspective is critical to identifying the executives whose work and impact truly stand out across the region.”
David Cass, President, CISOs Connect™ and CISO, Grayscale Investments
A global community
For CISOs Connect™, the APAC C25™ reflects the increasingly global nature of the issues confronting CISOs and their equivalents and the importance of bringing together perspectives from different markets, industries and regulatory environments.
It also extends the broader mission of CISOs Connect™: creating opportunities for security executives to learn from one another, elevate the work being done across the profession and build relationships that cross industries, markets and geographic boundaries.
“This is our inaugural APAC C25™, so it is also an opportunity to establish what this recognition will stand for. We want the first class to reflect the depth and diversity of leadership across Asia Pacific and set a standard that is meaningful to the executives who do this work every day.”
Aimee Rhodes, CEO, CISOs Connect™
Nominations · No fees
Nominations for the inaugural APAC C25™ open Nov. 4, 2026, and close Nov. 30, 2026. Nominate a CISO or equivalent cybersecurity leader in Asia Pacific, or put yourself forward. There are no nomination or application fees.
The award ceremony
The inaugural APAC C25™ class will be celebrated in person in Singapore, with the option to join virtually.
For more information, email [email protected]
All Recognition ProgramsRecipient records for APAC C25™ are not published yet. Honorees are added here as each class is announced.
We believe exceptional communities are built through exceptional members. Our goal isn’t to create barriers to joining — it’s to ensure every member shares a commitment to collaboration, professionalism, and helping fellow cybersecurity leaders succeed. The application is intentionally brief: a CISOs Connect™ member of the curation team follows up.